- US-Bound Oil Supertanker Breached by Hackers
 on October 6, 2026
While approaching the coast of Texas, an oil supertanker was hacked.
- Frontline Education Data Breach Highlights Third-Party Risks
 on October 6, 2026
An education technology company was breached.
- LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings
 on October 6, 2026
A malicious spreadsheet can make LibreOffice and Apache OpenOffice run an attacker's code as soon as the file is opened, security researchers have shown. There is no warning first, of the kind either program shows before it runs a macro. The attack works only when the program's Java support is enabled. So far, it has only been shown as a proof of concept, and there are no reports of its use in
- Here’s how experts think CISA should tell agencies to protect OT
 on October 6, 2026 in Government, Policy, Binding Operational Directive, Cybersecurity and Infrastructure Security Agency (CISA), Federal IT, Michael Garcia, National Security Agency (NSA), operational technology, Operational Technology Cyber Coalition, water sector
Government auditors say federal agencies haven’t met mandated security steps for operational technology, which hackers targeted in water sector attacks this summer. The post Here’s how experts think CISA should tell agencies to protect OT appeared first on CyberScoop.
- Wikimedia Says OpenAI Agents Tried to Compromise Etherpad and Use Wiki Tools as Proxies
 on October 6, 2026
The Wikimedia Foundation, which hosts Wikipedia, has confirmed that it has discovered activity by rogue OpenAI agents on its platforms, including unsuccessful efforts to compromise Etherpad, a public note-taking tool, and edit Wikipedia pages. "The unauthorized bot activities included edits to our wikis, some unsuccessful attempts to exploit a public note-taking tool we host, and heavy traffic,
- Welcome to the Jungle: What We Found Inside 15,465 Public MCP Servers
 on October 6, 2026
In 2024, MCP (Model Context Protocol) set out to become the USB-C of AI: one standard for connecting models, agents, and IDEs to tools and data. The protocol delivered. Thousands of developers built servers, and enterprises plugged them into agent workflows. The ecosystem around it fell short. Earlier this year, our team at OX Security, traced critical vulnerabilities in Anthropic's MCP
- Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports
 on October 6, 2026
Google has stopped accepting product vulnerability reports through its bug bounty program for its open-source software. The change, in effect since October 1, means researchers can no longer submit security flaws in the code of projects such as Go, Angular, and Protocol Buffers there for a reward. Reports about supply chain compromises are still accepted, and reports filed before October 1 are
- Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products
 on October 6, 2026
A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in each product's web application root directory. The attacker must already know a file's exact name and path and cannot list what the directory holds. Atlassian disclosed the flaw, CVE-2026-21589, on October 5, rated it 9.3 out of 10, and
- FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach
 on October 6, 2026
The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of personal details of thousands of bureau employees. That's according to a report from Reuters, citing two sources familiar with the matter. "To date, our review has determined that the incident occurred as the result of a security failure
- Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account
 on October 6, 2026
Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark's national population register, the country's digitalization ministry said on October 5. They used a private Danish company's lawful right to look up records in the Central Person Register (CPR). The ministry has told people never to
- ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits
 on October 6, 2026
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser's cache. "Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file," the Microsoft Threat Intelligence team said in a post on X.
- Citrix discloses third actively exploited NetScaler zero-day in less than a weekon October 5, 2026 in Cybersecurity, Research, Threats, Citrix, Citrix NetScaler, Coalition, Cybersecurity and Infrastructure Security Agency (CISA), vulnerabilities, vulnerability disclosure, vulnerability reporting, watchTowr, zero-day, zero-day exploit
The vendor was much quicker and consistent in its response to the latest defect, and researchers consider the impact relatively low compared to the previous pair of zero-days. The post Citrix discloses third actively exploited NetScaler zero-day in less than a week appeared first on CyberScoop.
- Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users' Mailboxes
 on October 5, 2026
Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain conditions. The vulnerability, tracked as CVE-2026-96940, is rated 8.8 on the CVSS scoring system. "Weak authorization in Microsoft Exchange Server allows an authenticated attacker to elevate privileges over a
- Why Location Intelligence is Becoming Critical for Emergency Response and Security Operations
 on October 5, 2026
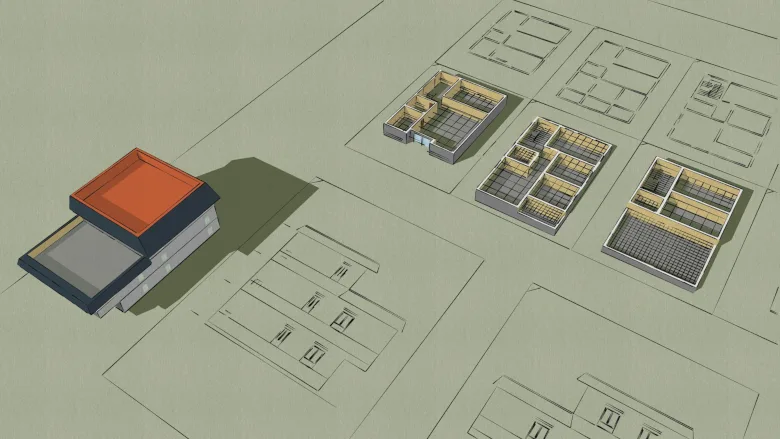
When an alarm triggers and the operator can see the event pinned to a specific room on a live 3D indoor map, the response changes fundamentally.
- ⚡ Weekly Recap: NetScaler and FortiMail 0-Days, AI Coding Leaks, Spectre v2 and Ransomware Arrests
 on October 5, 2026
A blank field. A public repo. One reply to an email. A box left exposed. None of this sounds dramatic, which is partly the problem. This week’s threats keep finding leverage in small things that were easy to overlook. There are actively exploited bugs in the mix, cleaner intrusion paths, smarter automation, and a long patch list waiting behind them. Some attacks are getting more capable. Others
- The Credential Layer Is Expanding Faster Than Security Teams Can See It
 on October 5, 2026
Every modern enterprise depends on credentials. This is how humans, systems, and now AI, all connect to data, services, and each other securely. GitGuardian helps secure that credential layer through three connected capabilities: Detect, Remediate, and Prevent. The journey starts with detection, because organizations first need to understand what credentials exist, where they live, and what they
- Realtek Jungle SDK Exploit Attempts Deliver Cling Botnet With STUN-Based C2
 on October 5, 2026
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet malware called Cling. "Cling is notable not because it introduces a new propagation technique, but because it repurposes ordinary STUN behavior into a practical command-and-control channel," Nozomi Networks said in a report
- Apple Plans Tighter macOS Full Disk Access Controls Over AI Agent Data Access
 on October 5, 2026
Apple has announced that it's taking steps to tighten controls around a macOS setting called Full Disk Access (FDA) due to security risks posed by artificial intelligence (AI) agents. "Some developers are using Full Disk Access in ways that could put users at risk, exposing everything on their systems—including files, mail, messages, and even browsing history – without users' full knowledge
- The US needs a real plan to defend its water systemson October 5, 2026 in Commentary, Artificial Intelligence (AI), code-mending, Congress, formal verification, op-ed, operational technology, Rockwell, Schneider Electric, Siemens, Trump administration, water sector
Here’s what it would take: stronger defenses for large utilities, hands-on help for smaller systems and federal support to make both happen. The post The US needs a real plan to defend its water systems appeared first on CyberScoop.
- Attackers Target Rejetto HFS Flaw That Enables Admin Session Forgery and RCE
 on October 5, 2026
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS score: 9.3), a case of session forgery stemming from the use of a weak pseudo-random number generator (PRNG) that can lead to a predictable key, which an attacker can then use to gain unauthorized access and
- New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline
 on October 5, 2026
Citrix has released security updates for a high-severity security flaw in NetScaler ADC and NetScaler Gateway that has been exploited as part of targeted zero-day attacks. The vulnerability, tracked as CVE-2026-88779, carries a CVSS score of 8.7 out of 10.0. "CVE-2026-88779 is a memory overflow vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway that can lead to
- ShinyHunters Suspect Rey Reportedly Detained in Jordan, Helping FBI Identify Group Members
 on October 4, 2026
A suspected member of the ShinyHunters digital extortion group, who goes by the online alias "Rey," has been allegedly detained by authorities in Jordan, Reuters reported, citing three people familiar with the matter. Rey, whose real name is Saif al-Din Khader, is said to have been brought into custody on September 29, 2026, and cooperating with the U.S. Federal Bureau of Investigation (FBI)
- China-Aligned TA419 Targets U.S. AI Policy Experts With Microsoft AitM Phishing
 on October 4, 2026
A new China-nexus cyber espionage group known as TA419 has been attributed to multiple credential phishing campaigns targeting artificial intelligence (AI) experts working for U.S. think tanks, universities, and legal sector organizations. The campaigns have impersonated prominent economists and AI policymakers, as well as a prominent Anthropic employee, to single out an AI policy expert at a
- MI5 Says China’s MSS Funded Research Involving 100+ U.K.-Linked Academics
 on October 3, 2026
The U.K.'s domestic intelligence and security agency has warned that more than 100 academics have helped China boost its intelligence gathering efforts on behalf of Beijing's state security service. In a "Security Service Espionage Alert" issued on September 30, 2026, MI5 said the "primary purpose of the China General Technology Research Institute (CGTRI) 中国通用技术研究院 is to fund research that
- Warlock Exploits SharePoint Flaws to Disable Security Tools and Deploy Ransomware
 on October 3, 2026
The suspected China-linked threat actor known as Warlock is still continuing to weaponize Microsoft SharePoint vulnerabilities, likely both old and new, in attacks targeting organizations in Portuguese- and Spanish-speaking countries. The activity, observed by the Symantec and Carbon Black Threat Hunter Team, has hit critical infrastructure, government, and education organizations. "In the
- The State of Cybersecurity in 2026: Key Segments, Insights, and Innovations
 on October 3, 2026
Featuring: Cybersecurity is being reshaped by the expansion of cloud infrastructure, AI, distributed systems, and increasingly complex digital environments. As organizations manage more identities, devices, data, and internet-facing infrastructure, security is shifting toward continuous visibility, control, and the ability to respond to risk at scale. This report examines how core areas of
- The legal questions raised by agentic AI hackson October 2, 2026 in AI, Cybersecurity, Government, Policy, Technology, Agentic AI, AI hacking, Anthropic, Computer Fraud and Abuse Act (CFAA), Federal Trade Commission (FTC), Google, lawsuit, legal, Meta, OpenAI
Experts and policymakers want AI companies to face consequences for agentic hacks. There may not be a clear-cut answer under existing laws and regulations. The post The legal questions raised by agentic AI hacks appeared first on CyberScoop.
- GitLab Patches Critical 9.9 AI Gateway Flaw Allowing Command Execution on Self-Hosted Servers
 on October 2, 2026
A critical flaw in GitLab's AI Gateway could let a logged-in user with Duo Agent Platform access run commands on the gateway under certain conditions, GitLab said in an advisory. The gateway is the service that connects a GitLab instance to AI models, and only organizations that host their own gateway need to act. The flaw is fixed in gateway versions 19.2.4, 19.3.2, and 19.4.1. The flaw
- Antino Backdoor Uses Outlook and OneDrive for C2 in China-Nexus Espionage Campaign
 on October 2, 2026
Government and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino. Cisco Talos is tracking the cluster
- Dell CSM Flaws Enable Unauthenticated Admin Access and Root on Kubernetes Nodes
 on October 2, 2026
Dell has released security updates to address multiple critical security flaws in Dell Container Storage Modules (CSM) that could be exploited by bad actors to take over susceptible systems. The vulnerabilities are listed below - CVE-2026-63688 (CVSS score: 10.0) - A missing authentication for critical function vulnerability in the csm-authorization-storage gRPC server that an
- Jackie Bean Named Executive Director of SDM & Security Magazines
 on October 2, 2026
Jackie Bean has been named the Executive Director of SDM and Security Magazines.
- AI Risk Is Here, but Not in the Way You Might Expect
 on October 2, 2026
Focusing solely on AI, and not what AI will become a force multiplier of, won’t help us minimize loss and disruption.
- OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling
 on October 2, 2026
OpenAI has parted ways with three members of its safety team after they leaked private information in violation of company policies, The Wall Street Journal reported. "We have parted ways with three individuals for violating our policies on accessing and handling sensitive company information," a spokesperson for the company was quoted as saying. "Our investigation confirmed that these
- Why CISOs Struggle to Answer the Board's Three Hardest Questions, and How to Fix the Report
 on October 2, 2026
The quarterly board meeting is two weeks out. The security team is pulling exports from the identity provider, the cloud posture tool, the vulnerability scanner, the SIEM and the EDR console. Someone is building a spreadsheet to reconcile them. Someone else is turning that spreadsheet into slides. Then a board member asks three questions: How secure is the organization, overall? What is
- Disinformation, Defense and Democracy: A Look as This Year’s Election Security
 on October 2, 2026
Securing the electoral process is essential to ensuring Americans’ voices are heard, and that they trust they have been heard.
- Preventing AI Data Breaches and Leaks
 on October 2, 2026
Approximately 612,000 UK businesses experienced a cybersecurity breach in the past year, according to the UK Government's Cyber security breaches survey with OpenAI and Anthropic most recently having committed data breaches from uninstructed cyberattacks.
- Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility Tools
 on October 2, 2026
Google has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and financial fraud, the tech giant said the move would block a major attack pathway. Advanced Protection is a
- Critical FortiMail Zero-Day Flaw Exploited in Attacks Allows Unauthenticated Arbitrary File Writes
 on October 2, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-104286 (CVSS score: 9.8), allows unauthenticated attackers to write arbitrary files on the underlying system. "An improper
- Authorities seize KillSec extortion group infrastructure, arrest 3 alleged memberson October 1, 2026 in Cybercrime, Cybersecurity, Ransomware, cybercrime, Department of Justice (DOJ), Europol, extortion, extradition, Federal Bureau of Investigation (FBI), KillSec, ransomware
The teenager-run cybercrime group victimized roughly 500 organizations in less than two years. The post Authorities seize KillSec extortion group infrastructure, arrest 3 alleged members appeared first on CyberScoop.
- National cyber director: Government-industry collaboration vital to managing AI risks, competition with nationson October 1, 2026 in Government, Policy, Geopolitics, AI, Anthropic, Artificial Intelligence (AI), China, critical infrastructure, Cybersecurity and Infrastructure Security Agency (CISA), Department of Defense (DOD), health care, hugging face, Moonshot AI, National Cyber Director, National Institute of Standards and Technology (NIST), OpenAI, OSTP
Sean Cairncross talked about regulations, China, pilot projects and more Thursday. The post National cyber director: Government-industry collaboration vital to managing AI risks, competition with nations appeared first on CyberScoop.
